
Updated 22 October 2026, one day after the PHP security releases.
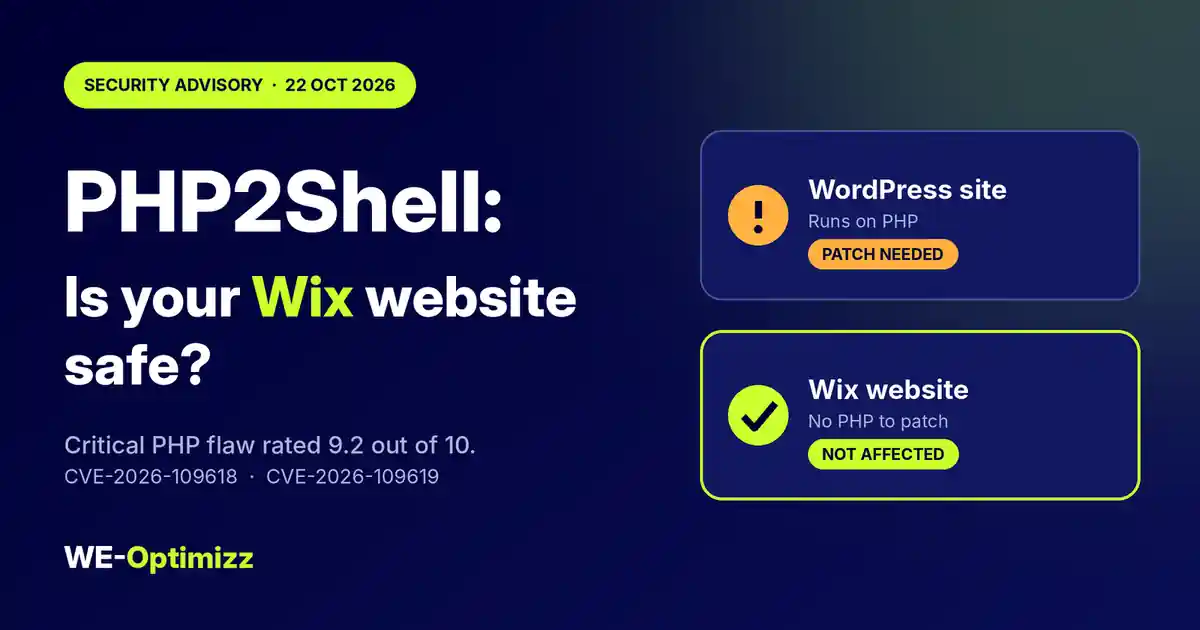
Your Wix website is not exposed to PHP2Shell. Wix does not let you run PHP code on a site, and you manage no server that needs the fix. WordPress, WooCommerce, Joomla, Drupal and Magento sites do run on PHP, so their hosting must move to a fixed version: PHP 8.5.12, 8.4.27, 8.3.36, 8.2.35 or later.
On 21 October 2026 the PHP team released emergency fixes for two critical flaws known as PHP2Shell. Since then we get the same question from business owners every hour: is my website next?
If your site runs on Wix, you do not have to patch anything for this one. If it runs on WordPress or another PHP system, the picture is different, and this article tells you what to do about it. For the first hours of the announcement, read our earlier PHP security advisory.
What is PHP2Shell?
PHP2Shell is the nickname for two critical security flaws in PHP itself, tracked as CVE-2026-109618 and CVE-2026-109619. PHP is the programming language that builds the pages of a WordPress site on the server before they reach your visitor. Both flaws score 9.2 out of 10. According to the researchers who disclosed them, they can let an attacker run code on a server without logging in.
The cause is memory handling. When PHP hits an error halfway through a web request, for example because it runs out of memory, it can later reuse data that was never set up properly.
That makes this different from the usual plugin problem. The bug is not in WordPress, your theme or a plugin. It sits in the engine underneath them. Automattic pointed out that updating WordPress, a theme or plugins does not close it. The server has to run a fixed PHP version.
What is confirmed so far
- Fixed releases exist. PHP published 8.5.12, 8.4.27, 8.3.36 and 8.2.35 on 21 October 2026.
- There is no complete workaround. The PHP team says updating is the only safe choice.
- The scope is wide. Any PHP installation that serves web requests is in scope until it runs a fixed version. Researchers believe the flaws reach back to PHP 5.4.
- PHP is everywhere. Roughly 69% of websites with a known server-side language use it, which is why the news spread so fast.
- Firewalls help, but do not fix. Cloudflare switched on default WAF protection for free and paid customers on 21 October. Treat that as an extra layer while you update.
Why a Wix website is not affected
Three facts explain it. None of them depend on luck.
1. A Wix site does not run PHP
Wix states in its help center that you cannot add PHP code to a Wix site. The platform supports HTML and JavaScript through Velo. PHP2Shell needs a PHP runtime that answers web requests. A Wix site does not have one that you control.
2. There is no server for you to patch
With WordPress, you or your host own the whole stack: operating system, web server, PHP version and database. With Wix, that layer belongs to the platform. Wix reports a dedicated security team, ISO 27001, SOC 2 Type 2 and PCI DSS Level 1 credentials, DDoS mitigation and TLS 1.2 or higher on every site.
You do not wait for a host to schedule an upgrade. You do not choose between a patch window and a website that stays online.
3. There is no plugin folder on a server you manage
A WordPress site collects plugins, themes and custom code that all depend on the PHP version underneath. A Wix site uses apps and features that run inside the platform. Your update list is shorter, and a runtime emergency does not become your emergency.
PHP site versus Wix site at a glance
| PHP site (WordPress, WooCommerce, Joomla, Drupal, Magento) | Wix website | |
|---|---|---|
| Runs on PHP | Yes | No. Wix does not support PHP code on sites |
| Affected by PHP2Shell | Yes, until PHP is on a fixed version | Not through PHP |
| Who updates the server | You or your hosting provider | The platform |
| Action needed this week | Check PHP version, update, test | None for PHP2Shell |
| Risk of forced downtime | Possible if you cannot patch in time | Not because of this flaw |
| Your remaining job | All of the above, plus plugins, themes and backups | Account security, custom code, third-party scripts |
Running a PHP site and tired of being on call for it? Tell us about your website and we will tell you honestly whether a move makes sense.
Not affected does not mean invincible
We would not be doing our job if we told you a Wix site can never have a security problem. PHP2Shell is a PHP problem. The risks that remain are mostly about people, not servers.
- Account takeover. Use a strong, unique password and switch on two-step verification for your Wix account.
- Too many collaborators. Give each person the lowest role they need and remove access when a project ends.
- Phishing and fake specialists. Scammers pose as Wix experts to get into accounts. Read how to spot a fake Wix specialist.
- Custom code and third-party scripts. Velo code, embedded HTML and tracking scripts are your responsibility. Review what runs on your pages.
If your site runs on PHP: what to do this week
- Find out what you run. WordPress, WooCommerce, Joomla, Drupal, Magento and most custom shops use PHP. Not sure? Ask your developer or hosting provider.
- Check your PHP version. Ask your host, or in WordPress open Tools, then Site Health, then Info, then Server.
- Compare it with the fixed versions. You need 8.5.12, 8.4.27, 8.3.36, 8.2.35 or later. Older branches are no longer supported by PHP, so ask your host about a backported fix or move to a supported version.
- Make a full backup of files and database before you change anything.
- Update PHP and test. Check forms, checkout, login and bookings. Old plugins sometimes break on a newer PHP version.
- Add a firewall layer such as a WAF while you update. It reduces exposure, it does not replace the update.
- Watch for warning signs. Unknown admin users, new files you did not upload or sudden traffic spikes mean you should call your host straight away.
Should you move from WordPress to Wix?
Sometimes yes. Often it is the sensible call. Not always.
A move makes sense when your site is a business, service or booking website, or a small to mid-size shop, and nobody on your team wants to own server updates. Staying on PHP can be the right choice for complex custom applications, setups that depend heavily on specific plugins, or teams with a developer and a host that patches within hours. Our comparisons of Wix vs WordPress for small business and Wix Studio vs WordPress SEO go deeper.
The real risk in a move is not the platform. It is losing the rankings you built. A careful migration protects them:
- Inventory everything. Pages, images, forms, integrations and the URLs that already bring in traffic.
- Map every old URL to its new one and set up 301 redirects, so Google and your visitors land on the right page.
- Rebuild in Wix Studio with titles, headings, structured data and internal links carried over.
- Test, launch and monitor. Check mobile and desktop, then follow Search Console for the first weeks.
See how our website migration and SEO migration work, or read more about building on Wix Studio. If you run a webshop, our e-commerce websites page explains what changes for checkout and payments.
Why WE-Optimizz
A website that looks good but is hard to find wastes your money. A website that is found but does not convert wastes your traffic. We build for both. We are a Wix Legends Partner with Wix Design and Wix Development certifications and a Wix Accessibility certification. We have delivered more than 900 websites for clients in over 35 countries, and we combine design with technical SEO and GEO, so a migration keeps your rankings and gets you cited in AI answers.
Key takeaways
- PHP2Shell (CVE-2026-109618 and CVE-2026-109619) is a critical flaw in PHP itself, scored 9.2 out of 10.
- Wix does not support PHP code on sites and manages the servers, so a Wix website has nothing to patch for this flaw.
- WordPress, WooCommerce, Joomla, Drupal and Magento sites need PHP 8.5.12, 8.4.27, 8.3.36, 8.2.35 or later.
- Updating WordPress or its plugins does not fix PHP. The server must be updated.
- Not affected is not the same as invincible. Protect your Wix account and review custom code.
- If you move from WordPress to Wix, plan redirects first so you keep your rankings.
Book a free discovery call. We will tell you whether you are exposed, what a fix would take and whether moving to Wix makes sense for your business. No pressure, no jargon.
Sources
- PHP 8.5.12 security release notes (php-src on GitHub)
- PHP 8.4.27 security release notes (php-src on GitHub)
- Imperva: PHP2Shell vulnerability analysis
- Cloudflare: protections against php2shell
- Newsweek: PHP vulnerability and affected websites
- Wix Help Center: using PHP on a Wix site
- Wix Help Center: Wix security measures overview
Written on 22 October 2026. Details about affected versions and exploitation can change. Check php.net for the latest guidance.
Frequently asked questions
No, not through PHP. Wix does not support PHP code on sites and manages the servers itself, so there is no PHP runtime for you to patch. Account security and custom code remain your responsibility.